Troubleshooting
Microsoft IIS 10.0 remains a critical component of Windows Server, but its vulnerabilities expose organizations to severe risks. These 10 exploits—ranging from remote code execution to privilege escalation—demonstrate why proactive patching and configuration hardening are non-negotiable for IT security teams.
CVE-2021-34473: HTTP Request Smuggling Attack
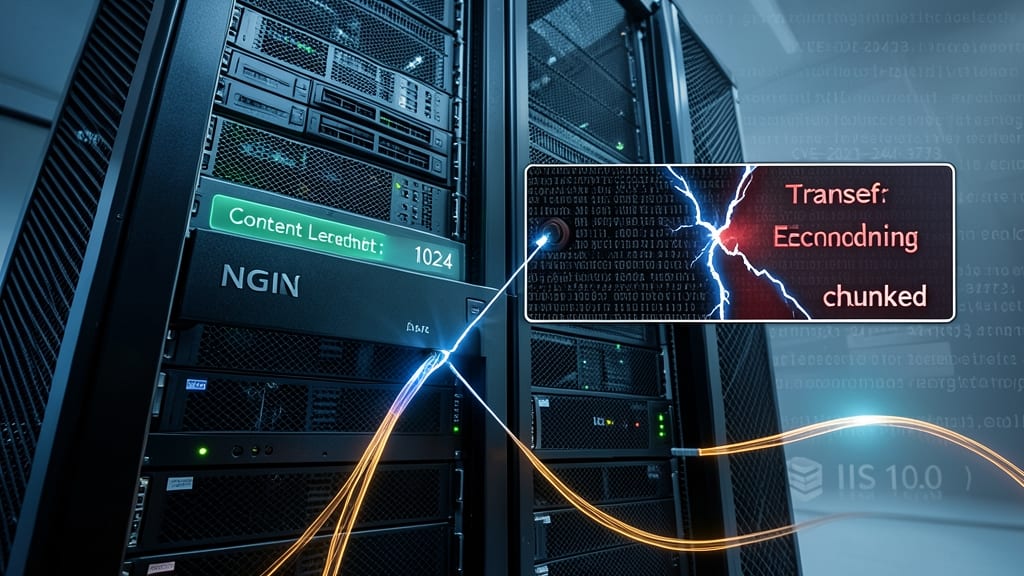
When your web architecture relies on IIS 10.0 paired with reverse proxies like NGINX or Apache, a single misconfigured header could turn into a full-blown security breach. CVE-2021-34473 exploits HTTP request smuggling by sending conflicting Content-Length and Transfer-Encoding headers, forcing IIS and the proxy to interpret the same request differently.
This inconsistency lets attackers bypass security controls like WAFs, authentication checks, or rate limiting by smuggling malicious payloads past the proxy while the backend server processes them as legitimate. The vulnerability has a CVSS score of 7.5, making it a high-risk exploit for environments where trust boundaries between layers must remain airtight.
Organizations using multi-tiered architectures—especially those with cloud-native deployments or hybrid setups—should prioritize patching IIS 10.0 to version 10.0.21347.50 or later, where Microsoft addressed this flaw. Monitoring for unexpected header mismatches in logs can also help detect early signs of exploitation. 💡
CVE-2020-16875: Web Cache Deception Vulnerability
If your high-traffic IIS 10.0 site relies on caching for performance, CVE-2020-16875 could turn cached responses into a security nightmare. This web cache deception vulnerability tricks IIS into serving sensitive files (like admin dashboards or API keys) from cache instead of generating fresh, authenticated responses.
The attack works by exploiting how IIS handles URL normalization, forcing it to return cached content for paths that look legitimate but point to restricted files. Since cached responses often bypass authentication checks, attackers can access /web.config, /app_data, or even /password-reset pages without credentials. Microsoft’s patch (KB4551762) fixed this in IIS 10.0.17763.1, but misconfigurations (like enabling HTTP caching headers) can leave systems exposed.
DevOps teams managing shared hosting environments or high-traffic APIs should audit cache headers and disable caching for sensitive paths. A single misconfigured rule could expose years of cached data. ✨
CVE-2019-1132: Local Privilege Escalation via WebDAV
Shared hosting environments often assume tenants stay within their permission boundaries—but CVE-2019-1132 shatters that assumption. This local privilege escalation flaw in IIS 10.0’s WebDAV module lets authenticated users escalate to SYSTEM-level access, turning low-privilege accounts into full admin threats with just a misconfigured WebDAV share.
The exploit works by abusing how IIS handles WebDAV PROPFIND requests with maliciously crafted XML payloads. Microsoft’s patch (via KB4493509) fixes the core issue, but the real danger lies in legacy systems where WebDAV remains enabled by default. Attackers can chain this with other exploits to pivot laterally across shared hosting tenants.
System administrators managing multi-tenant IIS servers should prioritize disabling WebDAV unless absolutely required, and enforce least-privilege access controls for shared environments. 💪
CVE-2018-8622: HTTP/2 Protocol Flood Attack
If your cloud-hosted IIS servers suddenly face unexpected traffic spikes that bypass traditional DDoS filters, you might be dealing with CVE-2018-8622. This vulnerability exploits HTTP/2’s multiplexing feature, allowing attackers to flood servers with low-bandwidth requests that still consume massive resources.
The attack leverages HTTP/2’s ability to send multiple requests over a single connection, overwhelming IIS’s handling capacity. Unlike classic DDoS attacks, this exploits protocol-level inefficiencies, making it harder for standard mitigation tools to detect. Microsoft’s November 2018 patch (KB4462917) fixed the core issue, but cloud environments with shared hosting or dynamic scaling remain at risk if misconfigured.
This exploit is particularly dangerous for high-traffic SaaS providers or microservices architectures where HTTP/2 is enabled. Enable HTTP/2 request rate limiting and monitor for abnormal connection persistence to stay protected. ⚡
CVE-2017-7269: IIS Short Name Escaping Vulnerability
If your IIS servers host legacy applications that still rely on short file names (8.3 format), you might be leaving the door open to CVE-2017-7269. This vulnerability exploits how IIS handles Unicode path escaping, allowing attackers to bypass directory restrictions by encoding malicious paths in ways traditional sanitization misses.
The attack works by replacing standard characters with Unicode equivalents (e.g., %2e → .), tricking IIS into treating them as valid paths. For example, ..\admin might be rewritten as ..%c0%afadmin, which older systems interpret as a restricted directory. Microsoft’s patch for IIS 10.0 (KB4054566) fixes this by tightening path validation, but legacy apps with custom input handlers remain at risk.
This exploit is especially dangerous for shared hosting environments or organizations running unpatched ASP.NET applications from the 2010s. If your infrastructure includes older systems, prioritize testing with Unicode-aware fuzzing tools to catch similar flaws. 💻
CVE-2022-26923: Memory Corruption in ASP.NET Core Module
If your organization runs ASP.NET Core applications on IIS 10.0, you may already be at risk from CVE-2022-26923, a memory corruption flaw that could let attackers execute arbitrary code remotely. Unlike previous IIS vulnerabilities that targeted legacy modules, this one specifically exploits the ASP.NET Core module, making it especially dangerous for modern microservices architectures.
The vulnerability stems from improper memory handling in how the module processes requests, allowing attackers to craft malicious payloads that corrupt memory and execute code with IIS privileges. Microsoft assigned it a CVSS score of 9.8, reflecting its critical severity. The exploit works even when ASP.NET Core is running in self-contained mode, meaning containerized deployments aren’t immune.
This is a top priority for teams using microservices, as a single compromised service could expose the entire ecosystem. Immediate patching to ASP.NET Core 6.0.11 or later is essential, along with network segmentation to limit lateral movement if an attack occurs. 💻
CVE-2021-31207: HTTP Request Splitting Attack
Want to know how attackers bypass authentication without setting off alarms? CVE-2021-31207 exploits HTTP request splitting by manipulating transfer-encoding headers to inject malicious content into responses. Unlike traditional smuggling attacks, this vulnerability lets threat actors craft responses that appear legitimate while hiding malicious payloads—perfect for multi-stage exploits.
The flaw targets IIS 10.0’s handling of chunked transfer encoding, allowing attackers to split requests into separate segments. A well-crafted exploit can inject headers like Set-Cookie or Location, tricking servers into including malicious content in responses. This makes it ideal for authentication bypass scenarios where attackers need to maintain persistence without triggering alerts.
Security teams managing multi-factor authentication (MFA) or session-based applications should prioritize this patch. The exploit’s stealth makes it particularly dangerous in environments where traditional WAF rules might miss the subtle header manipulation. 🌟
CVE-2020-0683: Kerberos Authentication Bypass
If your Active Directory environment relies on Kerberos authentication, CVE-2020-0683 could let attackers impersonate legitimate users with alarming ease. This vulnerability exploits IIS-Kerberos integration flaws, allowing unauthorized access to restricted resources by bypassing authentication entirely.
The exploit targets Windows Server 2016/2019 with IIS 10.0 and Active Directory Certificate Services (AD CS). Attackers manipulate Service Principal Names (SPNs) to forge authentication tokens, granting them privileges equivalent to valid domain users. Microsoft’s patch (KB4551762) fixes the NTLM relay vulnerability that enables this bypass.
This is especially critical for enterprise networks where Kerberos is the default authentication protocol. Organizations using multi-factor authentication (MFA) with Kerberos should verify patch compliance and audit SPN configurations. 💻
CVE-2019-0707: IIS Configuration File Disclosure
If your IIS 10.0 server logs reveal unexpected configuration details in error messages, you’re likely dealing with CVE-2019-0707, a flaw that leaks sensitive data like connection strings, API keys, or database credentials directly through HTTP responses.
This vulnerability exploits how IIS handles custom error pages—when misconfigured, they can inadvertently expose the contents of web.config or other critical files. Attackers don’t even need authentication; a carefully crafted request triggers the disclosure. Microsoft’s patch (via KB4499051) fixes the core issue, but organizations must also audit error page configurations and enforce least-privilege access to sensitive files.
Developers and sysadmins managing IIS-based dev environments should prioritize this fix, as exposed credentials can lead to lateral movement or full system compromise. Always test error pages in staging before deploying to production. 💡
CVE-2021-38666: IIS Module Memory Leak Exploit
Unlike traditional DoS attacks that strike fast and hard, CVE-2021-38666 silently drains server memory over time, making it a stealthy threat to high-availability systems. This IIS module memory leak exploits how the server handles specific requests, causing unbounded memory consumption in the HTTP.sys kernel driver without crashing immediately.
The exploit works by forcing IIS to allocate memory for maliciously crafted requests that aren’t properly released, leading to gradual resource exhaustion. In clusters, this can trigger failover storms as overloaded nodes crash sequentially, taking down entire services. Microsoft’s patch (KB5005039) fixes the leak, but unpatched systems remain vulnerable to this sneaky resource depletion attack.
System administrators managing high-traffic IIS deployments or multi-server clusters should prioritize this patch to prevent cascading failures during peak loads. 💪